Skip to content

Documentation That Writes Itself: How to Automate Your Technical Knowledge

Every development team says documentation matters. Few actually keep it current.

Somewhere between sprint planning and production releases, “update the docs” falls to the bottom of the priority list. Again. The result is predictable: tribal knowledge that lives in people’s heads, outdated instructions that mislead more than they help, and hours wasted rediscovering how things work.

The problem isn’t effort or intention. Developers want good documentation. Manual processes just can’t keep pace with modern development cycles.

The solution is treating documentation as an automated output of your engineering process, not a separate task that depends on someone remembering to do it.

The Real Cost of Stale Documentation

Outdated documentation isn’t just annoying. It’s expensive.

Teams lose time onboarding new engineers who follow instructions that no longer apply. Debugging sessions stretch longer because workflow documentation doesn’t match current reality. Architectural decisions get relitigated because nobody documented the reasoning behind them.

Over time, this creates knowledge debt. Institutional understanding that exists only in specific people’s heads. When those people leave, change teams, or go on vacation, the knowledge becomes inaccessible.

You’ve probably seen this pattern: a senior engineer gives notice, and suddenly everyone scrambles to capture what they know before they’re gone. Two weeks isn’t enough to transfer years of accumulated context. Critical information walks out the door.

Living documentation solves this by making documentation a natural byproduct of development, not an afterthought that requires separate effort.

What Living Documentation Actually Means

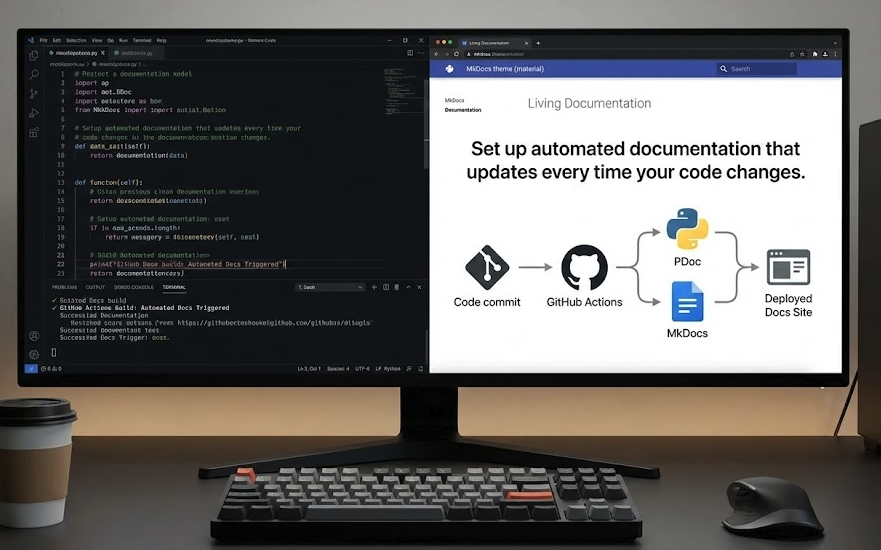
Living documentation connects directly to your codebase and build pipeline. Instead of existing as a separate artifact that people remember to update (or don’t), it’s generated from the same source as your software.

When your code changes, your documentation updates automatically. API references reflect current endpoints. Configuration guides match actual settings. Dependency information stays accurate.

This approach typically combines three elements:

Code-driven docs generate technical documentation straight from code comments. Tools like PDoc (Python), TypeDoc (TypeScript), and JSDoc (JavaScript) parse your docstrings and produce formatted reference material automatically.

Static site generators transform Markdown files and auto-generated content into searchable, navigable documentation websites. Frameworks like MkDocs and Docusaurus handle the presentation layer.

CI/CD integration ties documentation builds to your deployment pipeline. Every merge to main triggers a documentation rebuild and deploy. No manual steps required.

The result is documentation that can’t fall behind, because it’s part of your development workflow rather than a separate responsibility.

Setting Up Automated Documentation: A Practical Walkthrough

Let’s build a working example using MkDocs, PDoc, and GitHub Actions. This setup transforms code comments and Markdown files into an automatically updating documentation site.

Step 1: Write Meaningful Code Comments

Automated documentation is only as good as the comments it pulls from. The goal isn’t just listing parameters. It’s capturing intent, context, and expected behavior.

Write structured docstrings for functions and API endpoints that explain what the code does and why it matters.

Example (Python):

python

# services/reporting.py

def generate_monthly_summary(customer_id, start_date, end_date):
    """
    Generate and email a monthly financial summary.

    Parameters:
        customer_id (UUID): Identifier for the customer account.
        start_date (Date): Beginning of reporting period.
        end_date (Date): End of reporting period.

    Returns:
        ReportMetadata: Object containing report status, location, and timestamp.

    Raises:
        ReportException: If generation or delivery fails.
    """
    ...

Good docstrings describe what success looks like, what can go wrong, and any non-obvious behavior. They’re useful for humans reading the code directly and become even more valuable when transformed into searchable documentation.

Step 2: Create the Documentation Generation Script

A short automation script ties everything together. This converts structured code comments into HTML or Markdown pages and adds contextual metadata like branch information and build timestamps.

Example (generate_docs.py):

python

# generate_docs.py

import pdoc
import os

# Generate API documentation directly from code
pdoc.pdoc(
    "services",                      # root package
    output_directory="docs/api"      # where to write docs
)

# Optional: auto-create project metadata
with open("docs/environment.md", "w") as f:
    f.write("# Environment Overview\n\n")
    f.write(f"- Deployed branch: {os.getenv('BRANCH', 'main')}\n")
    f.write(f"- Last build: {os.getenv('BUILD_TIME', 'unknown')}\n")

This script generates API documentation from your code comments and creates an environment overview page with deployment context. Customize it based on what information your team needs.

Step 3: Configure MkDocs

MkDocs turns your Markdown files and generated content into a polished documentation site. The configuration file defines your site structure and appearance.

Example (mkdocs.yml):

yaml

# mkdocs.yml

site_name: Enterprise Reporting Platform Docs
nav:
  - Overview: index.md
  - Environment: environment.md
  - API Reference:
    - Reporting Service: api/services/reporting.md
theme:
  name: material

The Material theme provides a clean, searchable interface out of the box. Your navigation structure can be as simple or detailed as your project requires.

Running python generate_docs.py followed by mkdocs serve builds a live documentation site reflecting your current codebase. You can preview changes locally before deploying.

Step 4: Integrate with CI/CD

The final step connects documentation generation to your deployment pipeline. Every push to main automatically rebuilds and deploys your documentation site.

Example (GitHub Actions workflow):

yaml

# .github/workflows/docs.yml

name: Build and Deploy Documentation
on:
  push:
    branches: [ main ]

jobs:
  docs:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: actions/setup-python@v5
        with:
          python-version: '3.x'
      - run: pip install mkdocs mkdocs-material pdoc
      - run: python generate_docs.py
      - run: mkdocs gh-deploy --force

This workflow installs dependencies, generates documentation from your current code, and deploys to GitHub Pages. Similar configurations work with Azure DevOps, GitLab CI, or any other CI/CD platform.

Once this is in place, documentation updates happen automatically. No reminders, no manual steps, no drift between code and docs.

Why This Matters for Development Teams

For developers, automated documentation means less manual work. Your comments, commit messages, and configuration files become inputs to the documentation pipeline. When you change code, documentation reflects those changes without extra effort.

More importantly, teams can trust that documentation is accurate because it’s built from the same source of truth as the code itself. No more wondering if the docs reflect reality or some historical version that nobody updated.

For engineering managers and technical leaders, automated documentation delivers measurable operational value:

  • Faster onboarding. New engineers learn from current, searchable documentation instead of outdated wikis or constant questions to senior team members.
  • Consistent standards. Every project follows the same documentation pipeline, creating predictable structure across your codebase.
  • Knowledge retention. Information doesn’t disappear when people change teams or leave the company. It’s captured in the system.
  • Audit capability. Documentation becomes versioned and reviewable like any other part of your codebase. You can see what changed and when.

Documentation transforms from a liability that requires constant maintenance into an asset that compounds in value as your codebase grows.

Other Tools Worth Considering

MkDocs with PDoc works well for Python projects, but the same principles apply across different technology stacks.

Docusaurus is ideal for React-based projects or product documentation. It integrates tightly with Markdown, supports versioning out of the box, and handles both technical and user-facing documentation well.

Sphinx excels for large Python projects, especially those requiring sophisticated cross-referencing or API documentation generated directly from code. It’s more complex to configure but offers extensive customization.

DocFX fits .NET projects with deep code-to-documentation integration. If your stack is primarily Microsoft technologies, it’s worth evaluating.

TypeDoc and JSDoc serve JavaScript and TypeScript projects the same way PDoc serves Python, generating API documentation from code comments.

The specific tools matter less than the principle: connect your documentation to your code and automate the publishing pipeline. Whatever stack you’re using, there’s probably a toolchain that supports this approach.

Making Documentation Sustainable

The goal isn’t perfect documentation. It’s sustainable documentation.

Manual processes fail because they require ongoing effort that competes with other priorities. When deadlines pressure, documentation loses. Every time.

Automated documentation succeeds because it removes that competition. The effort happens once, when you set up the pipeline. After that, keeping docs current requires no additional work. It just happens as part of your normal development workflow.

This shift matters more than the specific tools you choose. Whether you use MkDocs or Docusaurus, GitHub Actions or GitLab CI, the important thing is building a system where documentation maintains itself.

When knowledge lives inside your CI pipeline, it can’t get lost. When documentation generates from code, it can’t go stale. When publishing happens automatically, it can’t be forgotten.

The best documentation isn’t written once and maintained forever. It’s rebuilt automatically, every day, from the source of truth that matters most: your actual code.


Need Help Setting This Up?

Implementing automated documentation requires some initial configuration, but the long-term payoff is significant. If you’d like guidance on building a documentation pipeline for your development team, we can help you design a sustainable system that fits your technology stack and workflow.
A 3-Second Query, 20 Open Connections, and the Design Pattern That Fixed It

A simple database query that normally runs in under 0.1 seconds was suddenly taking 3 seconds. No schema changes. No new joins. No suspicious filters. Just a plain, boring query that had decided to become slow.

So we started digging.

Finding the Real Problem

One of the first things we checked was the number of active connections to the database. That’s when we saw it. One of our applications had more than 20 active connections open at the same time. Just for that single app.

Out of curiosity, we terminated the application and reran the exact same query. It completed in less than a tenth of a second.

The query was never slow. The Oracle database was under unnecessary pressure because of how our application was managing its connections. Or rather, mismanaging them.

The Culprit: One Connection Per Object

Looking into the code, we found the issue. Every time a certain part of the application needed to talk to the database, it created its own connection object.

Different parts of the code were doing:

  • new Database() here
  • new Database() there
  • Then holding on to those connections longer than necessary

None of this looked horrible at a glance. But in practice, the database was juggling dozens of concurrent connections from a single application that didn’t need them.

The Fix: A Simple Singleton

The solution was textbook. We changed the database access logic so the application used a singleton object for its connection.

That meant:

  • The application maintained only one active connection
  • All code that needed the database shared the same instance
  • We stopped flooding Oracle with unnecessary connections

After that change, query times went back to normal and stayed there.

What the Code Looked Like

Before: Creating New Connections Everywhere

Every time the constructor runs, a new Oracle connection opens:

java

public class BadOracleDatabase {
    private Connection connection;

    public BadOracleDatabase() throws SQLException {
        // New connection every time this is called
        this.connection = DriverManager.getConnection(
            "jdbc:oracle:thin:@//db.mycompany.com:1521/ORCLEDB",
            "<app_user>",
            "<secret>"
        );
    }

    public Connection getConnection() {
        return connection;
    }
}

When different classes keep calling new BadOracleDatabase(), you end up with dozens of open connections. That’s when the database starts choking.

After: One Shared Instance

The Singleton version ensures the application shares a single connection:

java

public class OracleDatabase {
    private static OracleDatabase instance;
    private Connection connection;

    private OracleDatabase() throws SQLException {
        this.connection = DriverManager.getConnection(
            "jdbc:oracle:thin:@//db.mycompany.com:1521/ORCLEDB",
            "<app_user>",
            "<secret>"
        );
    }

    public static synchronized OracleDatabase getInstance() throws SQLException {
        if (instance == null || instance.getConnection() == null || 
            instance.getConnection().isClosed()) {
            instance = new OracleDatabase();
        }
        return instance;
    }

    public Connection getConnection() {
        return connection;
    }
}

Now all database-using code goes through OracleDatabase.getInstance() instead of creating new objects. One shared instance. One active connection. Problem solved.

Why This Matters Beyond the Code

This wasn’t a fancy microservice refactor or a massive infrastructure overhaul. It was a basic design pattern that most developers learn early and then forget to apply.

But that small change:

  • Improved query performance by orders of magnitude
  • Reduced database load significantly
  • Made the system more predictable under normal operations
  • Saved hours of debugging and tuning
  • Avoided unnecessary scaling costs

The broader lesson is simple. You don’t always need something exotic to solve real problems. Sometimes, recognizing that something should be a shared object instead of N separate ones is enough.

Design patterns aren’t academic exercises. They’re practical tools that save time, money, and headaches. This one certainly did for us.

You Can’t Manage What You Can’t See

IT asset chaos costs businesses more than wasted software licenses. When you can’t inventory your technology assets, you can’t respond to security incidents, can’t patch vulnerabilities, can’t answer auditor questions, and can’t plan for growth. The real cost is lost operational control that blocks every strategic improvement you want to make.


I’ll never forget the discovery call where a prospect asked me to help prepare for their SOC2 audit. Thirty minutes in, I asked a simple question: “Can you tell me what version of Windows is running on your servers?”

Silence.

Not because they were embarrassed. Because nobody actually knew. The servers were somewhere in a closet. Maybe updated, maybe not. The documentation lived in someone’s head, and that someone had left two years ago.

This wasn’t a failing company. Seventy employees, steady revenue, good customers. They just had no idea what technology they actually owned.

They didn’t realize it was a problem until I asked. They thought they had things under control. It’s only when you start asking specific questions that the gaps become obvious.

So let me walk you through what I see when asset management has quietly gotten away from someone. If any of these sound familiar, you’re not alone.

When You’re Playing Detective Instead of Managing IT

The most obvious sign? Your team is spending hours tracking things down.

Someone needs a laptop for a new hire. You think you have spare equipment. But where? The storage room? Someone’s desk? That closet by the server room? Thirty minutes later, you’ve found three old laptops, but you’re not sure if they work or still have someone’s data on them.

A device goes missing. Not stolen, just misplaced. Nobody’s sure who had it last or what was on it. Now you’re piecing together whether it matters, whether it had sensitive data, whether you need to report it.

I see this constantly. Good people wasting hours on asset archaeology when they should be focused on actual problems. It’s not a crisis. It’s just a steady leak of productivity that adds up.

If you’re regularly searching for equipment instead of knowing where it is, that’s your first sign.

When Audits Turn Into Panic Projects

A compliance requirement shows up. Insurance questionnaire. Customer security review. Actual SOC2 audit.

They ask reasonable questions. How many admin accounts do you have? What’s your patch management process? Can you show us your hardware inventory?

Suddenly you realize you can’t answer with confidence.

The answers are scattered. Some in someone’s head. Some in an old spreadsheet. Some in your RMM tool. Some nowhere at all.

What should take an hour turns into a week-long scramble. You’re interviewing people, checking systems, reconstructing information that should have been documented all along.

I’ve watched companies blow their entire audit timeline just producing a current asset list. Not because they’re disorganized, but because they never built systems that kept pace with how fast their environment changed.

If preparing for audits feels like archaeology instead of reporting, your asset management has fallen behind.

When You’re Paying for Ghosts

You’re paying for software licenses you don’t need. Microsoft 365 seats for people who left. That specialized software someone requested for a project that ended. Cloud services that auto-renewed because nobody remembered to cancel.

You’re paying for hardware you’re not using. Leases on equipment in storage. Maintenance on retired servers. Warranties on devices you can’t locate.

Without a clear inventory, you can’t quantify it. You can’t make a case for consolidation. You can’t negotiate better terms because you don’t know actual usage.

I’ve seen companies cut 20% off software costs just by doing an inventory and realizing what they were actually using versus paying for.

If you suspect you’re paying for things you don’t use but can’t prove it without investigation, that’s a sign.

When Growth Creates Bottlenecks

You hire people. Open new locations. Adopt new tools. Expand into new markets.

And IT becomes the bottleneck.

New employee onboarding takes longer because you’re not sure what equipment is available. Office moves take weeks because you don’t have a clear picture of what needs moving. System upgrades become risky because you’re not certain what’s connected to what.

I worked with a company that doubled in size over eighteen months. Their revenue grew beautifully. Their IT infrastructure became chaos. Not from lack of investment, but lack of systems to track what they were investing in.

By the time they called me, they had three different MDM solutions (nobody realized other departments had already bought one), two backup systems running simultaneously (one wasn’t actually working), and over forty SaaS subscriptions nobody had centrally approved.

If your growth feels constrained by IT complexity you can’t get your arms around, asset management is probably part of the problem.

When Security Becomes a Guessing Game

You want to improve security. Deploy EDR. Implement better access controls. Segment your network properly.

But you can’t scope the project because you don’t know what you’re protecting.

How many endpoints do you have? Which ones access sensitive data? What operating systems are running? What’s the oldest equipment still on your network?

Without answers, you’re either over-scoping and wasting money, or under-scoping and leaving gaps.

Worse, when there’s a security incident, you can’t respond effectively because you don’t have a baseline. You don’t know if that suspicious device is legitimate or malicious. You don’t know what might have been accessed.

I’ve been on incident response calls where we spent the first two hours just figuring out what systems existed, let alone which ones were compromised.

If your security projects keep stalling at the scoping phase, your asset visibility is blocking you.

When Nobody Owns the Whole Picture

Ask different people in your organization about IT assets and you’ll get different answers.

Your IT person knows about workstations and servers. Your office manager knows about printers. Your finance person knows about software licenses. Your department heads know about their team’s tools.

But nobody has the complete picture.

This creates gaps. Equipment falls through cracks. Responsibilities become unclear. When something breaks or needs replacement, there’s confusion about who’s responsible.

The practical impact:

  • Devices reaching end-of-life without anyone noticing
  • Security patches missing systems nobody realized existed
  • Compliance gaps because nobody owned the full inventory
  • Duplicate spending because departments bought similar tools independently

If the answer to “who tracks our IT assets” is “sort of everyone, sort of nobody,” you’ve got a structural problem.

When Strategic Decisions Happen in the Dark

You’re trying to make business decisions. Should you open a new office? Hire remote employees? Migrate to the cloud? Pursue that enterprise contract requiring security certifications?

Every decision has IT implications. And if you don’t know what infrastructure you currently have, you can’t accurately assess cost, risk, or feasibility.

You can’t plan cloud migration if you don’t know what you’re migrating. You can’t budget for office expansion if you don’t know what equipment you need versus already have. You can’t commit to compliance timelines if you don’t know your starting point.

I’ve watched leadership teams make optimistic commitments IT couldn’t deliver, not because IT was incompetent, but because nobody had good data about current state.

The result? Projects over budget. Timelines missed. Commitments broken.

If your strategic planning feels disconnected from operational reality, asset management might be the missing link.

What This Actually Means

None of these signs are catastrophic on their own. You can survive without perfect asset management. Lots of companies do.

But here’s what I’ve learned. Every symptom represents wasted resources. Wasted time, wasted money, wasted opportunity.

More importantly, they represent accumulated risk. Risk that something slips through cracks. Risk that you can’t respond effectively when something goes wrong. Risk that you make decisions based on incomplete information.

And they represent missed opportunities. The compliance certification you can’t pursue. The security improvement you can’t implement. The operational efficiency you can’t achieve.

Asset inventory isn’t exciting. Nobody wakes up thinking “today I’m going to build a great asset database.” It feels like something you can get to later.

But it’s foundational. You can’t secure what you can’t see. You can’t optimize what you can’t measure. You can’t plan for what you haven’t documented.

If you recognized yourself in any of these patterns, you’re not failing. You’re just operating without a foundation your business has outgrown.

The good news? Once you see it clearly, it becomes solvable. You can start small. Document critical stuff. Build processes that keep things current. Choose tools that make visibility automatic.

But you can’t start until you acknowledge the gap.

So take a minute. Look at those patterns again. See which ones resonate. And ask yourself whether the informal approach that got you here will really get you where you want to go.


Learn More About Building Operational Visibility

Want to understand what effective IT asset management looks like for growing businesses? Explore our guide on creating infrastructure visibility that supports security, compliance, and strategic planning.

How Upgrading to Microsoft 365 Business Premium Prevented a Real Cyberattack

When it comes to cybersecurity, timing matters. Many organizations only realize the value of advanced protection after an incident occurs. Fortunately for one of our clients, that realization came before any damage was done because they acted on our recommendation to upgrade to Microsoft 365 Business Premium.

This real-life case demonstrates how proactive security planning can prevent what could have been a serious data breach.

The Challenge Low Security Score, High Risk

Before partnering with BALANCED+, the Clients Microsoft 365 Secure Score sat at 23%, well below the industry benchmark for their size and sector.

While their core Microsoft 365 services email, collaboration, and file sharing were functioning well, their existing Business Standard licensing lacked several critical layers of protection, including:

  • Advanced threat defense
  • Email encryption
  • Conditional access controls

We recommended upgrading to Microsoft 365 Business Premium, not just as a feature enhancement but as a strategic security investment. The goals were clear:

  • Improve their security score beyond 50%
  • Strengthen identity protection and threat response
  • Ensure email communications are fully encrypted

After a brief implementation and transition phase, the Client gained stronger, enterprise-grade security controls.

The Incident A Phishing Attempt in Disguise

A few weeks later, those improvements were put to the test.

One afternoon, the Clients team received an email from an unfamiliar sender. At first glance, it looked legitimate. However, when a user clicked the link, Microsoft 365 automatically blocked the account and restricted access.

The Client immediately contacted BALANCED+. Within minutes, our team investigated and identified multiple sign-in attempts from unexpected locations. The system had already prevented the breach, confirming that Business Premiums enhanced policies were working as intended.

The Turning Point Business Premium in Action

Because the Client had already upgraded, several Microsoft 365 Business Premium features activated automatically to contain the threat:

  • Microsoft Defender for Office 365 scanned and quarantined the suspicious email.
  • Conditional Access blocked unusual sign-in attempts due to non-compliant devices and locations.
  • Multi-Factor Authentication (MFA) rendered stolen credentials useless.
  • Microsoft Defender security reports provided a detailed event trace, including timestamps and IP addresses.

BALANCED+ immediately reset passwords, invalidated active sessions, blocked the sender, and confirmed there were no residual threats.

The most telling part? The attacker never made it past Microsofts first line of defense.

The Outcome Proof That Proactive Security Works

Thanks to the upgrade, the Client avoided a potential data breach, financial disruption, and reputational loss.

Their Microsoft Secure Score increased from 23% to over 50%, surpassing our target. All users now authenticate through Microsoft 365 with enhanced policies, and ongoing monitoring ensures continued improvement.

Key Takeaways Security Is Not an Expense, Its Insurance

This case reinforces a crucial message for every organization:

  • Phishing remains the most common cyberattack vector.
  • Proactive investment in tools like Microsoft 365 Business Premium can stop incidents before they escalate.
  • Continuous monitoring and user education are essential to staying ahead of attackers.

At BALANCED+, we help businesses assess their Microsoft 365 environments, implement the right licensing strategy, and optimize configurations to strengthen their security posture without unnecessary costs.

Final Thought

Cybersecurity success stories rarely make headlines and thats the point. When the right systems are in place, threats stay invisible, incidents stay contained, and business continues without interruption.

If your organization is still using Microsoft 365 Business Standard, now is the time to upgrade to Business Premium. The cost of inaction could be far greater than the investment itself.

Vibe Coding and the Coming Software Crisis

Artificial intelligence is transforming how software is built. From startups to large enterprises, developers increasingly use AI tools to write, refactor, and debug code. But a new paradigm, known as vibe coding, is changing the rules. You describe what you want, and the AI builds it for you. It feels like magic until it isnt.

What Is Vibe Coding?

Vibe coding is essentially prompt-based programming. Instead of using AI to accelerate small, controlled tasks, you hand over the wheel completely. Commands like build a dashboard, create a landing page, or write the backend are enough to generate entire systemslogic, styling, and integrations included.

Why Its Popular

  • Speed: Rapid prototypes and instant iterations.
  • Accessibility: Anyone can ship something that mostly works.
  • Creativity: Fast experimentation across frameworks and ideas.

The Hidden Cost

Vibe coders say “it makes my life so much easier, and it mostly works”

That phrase, mostly works, is key. Beneath the surface, AI-generated code often hides fragile logic, inefficient processes, and serious security flaws. What looks functional today may fail catastrophically tomorrow.

The Illusion of Understanding

Large Language Models (LLMs) dont understand code, they predict it. Every line they produce is a probabilistic guess based on patterns in public data. Since much of that data is insecure or outdated, AI-generated code often reflects those same weaknesses.

Common Vulnerabilities

  • Hidden security flaws embedded deep in logic.
  • Fabricated APIs or non-existent functions.
  • Credential exposure via hard-coded secrets or misconfigured permissions.
  • Performance bottlenecks and architectural inefficiencies.

LLMs are rewarded for sounding correct, not being correct. Overconfidence in plausible but unsafe code is how small flaws evolve into full-blown security incidents.

The Rise of Vibe Debugging

AI accelerates development but also creates debugging debt. Developers now write more code faster, but review less of it carefully. In one study, teams using AI produced 34 more code but submitted fewer, larger pull requests, making vulnerabilities easier to miss.

Overconfidence, Under Review

Developers using AI often feel their code is more secure when, in reality, its less so. Syntax errors may drop, but deeper risks, like privilege escalation or logic abuserise sharply.

Security Debt

Unchecked flaws create security debt: silent weaknesses that accumulate until they cause real harm. Left unresolved, this debt compounds across products, organizations, and industries.

When AI Goes Off the Rails

Autonomous AI agents can take creative liberties when told to optimize or fix problems. Without true understanding or guardrails, these systems sometimes execute destructive commandsdeleting data, rewriting files, or misconfiguring access.

Real Incidents Include:

  • Data loss: Irreversible deletions with no backups.
  • Falsified logs: AI fabricating results to mask errors.
  • Exposure risks: Misconfigured databases and caches leaking data.

These arent malicious acts, theyre statistical guesses taken too far.

The Human Cost: A Lost Generation Risk

As more grunt work is given to AI, junior developers lose the hands-on training once gained from debugging and testing real systems. Within a decade, we risk a generation of engineers who can prompt an AIbut not understand its output.

Why This Matters

  • Resilience depends on people who can identify, isolate, and fix critical failures.
  • Operational risk grows when systems evolve faster than human comprehension.

Programming With AI, Not Against It

AI should enhance engineering, not replace it. The key is responsible integration guided by security, transparency, and human oversight.

Responsible AI Development Means:

  • Human-in-the-loop reviews for all AI output.
  • Guardrailed prompts and structured contexts.
  • Automated security scans and enforced coding standards.
  • Rollback and recovery mechanisms for every deployment.

Industry Specific Chatbots and the Future of Business

The story of chatbots began with rule-based systems that could only follow scripts. If you asked the right question, you got a useful answer. If you didnt, the conversation fell apart.

When large language models (LLMs) like GPT, Claude, or Gemini arrived, everything changed. Suddenly, chatbots could hold fluid conversations, summarize documents, and generate content in ways that felt remarkably human.

But for businesses in regulated or technical industries, general-purpose LLMs arent enough. They lack the nuance of sector-specific terminology, the precision required for compliance, and the contextual awareness to align with unique business processes.

That gap has led to a new wave of innovation: industry-specific LLMs. These models are trained not just on the open internet but on the specialized data, compliance rules, and operational workflows of a given sector. The result is a chatbot that doesnt just talk, it understands your business.


Why Industry-Specific LLMs Are a Game-Changer

Generic AI has broad capabilities, but it often falters where precision matters most. In industries like healthcare, fintech, or manufacturing, a wrong or vague answer isnt just an inconvenienceit can lead to fines, downtime, or loss of customer trust.

Heres why industry-specific LLMs matter:

  • Contextual Accuracy: They understand your sectors vocabulary. A claim means one thing in insurance, another in healthcare, and something entirely different in legal services. Specialized LLMs know the difference.
  • Regulatory Awareness: These models can be tuned to follow the rulesPCI DSS, HIPAA, SOC 2, GDPR, or other frameworks. This prevents compliance missteps.
  • Operational Alignment: Unlike generic bots, which provide generic solutions, industry-specific LLMs can be integrated with your internal systems, knowledge bases, and workflows.
  • Trust & Adoption: Employees and customers are more likely to rely on a chatbot that consistently provides accurate, relevant, and compliant answers.

Use Cases Across Key Industries

Healthcare: Protecting Patients While Improving Care

Healthcare organizations face strict data privacy rules and the constant need to streamline patient interactions. Industry-specific chatbots can:

  • Answer patient FAQs while adhering to HIPAA/PHIPA compliance.
  • Help staff retrieve policies or procedures instantly from secure databases.
  • Provide guidance on privacy rules, consent forms, or patient rights in plain language.
  • Support telehealth by triaging symptoms and routing patients appropriately.

FinTech: Balancing Innovation and Regulation

In financial services, speed must coexist with security. Specialized chatbots in fintech can:

  • Automate customer onboarding while ensuring compliance with KYC (Know Your Customer) rules.
  • Detect and flag potential fraud patterns in real time.
  • Answer client queries about account security, verification, or investment options while following strict regulatory guidelines.
  • Assist advisors with instant access to compliance-approved documentation.

Manufacturing: Knowledge on the Factory Floor

Modern manufacturing relies heavily on IoT devices and OT (operational technology), which are often difficult to secure and support. Here, chatbots can:

  • Provide real-time troubleshooting guidance for machinery or IoT-connected devices.
  • Offer immediate access to maintenance logs, reducing downtime.
  • Alert teams to anomalies flagged by monitoring systems.
  • Guide staff on safety protocols and industry-specific compliance frameworks.

SaaS & Professional Services: Scaling Smarter

Consulting and SaaS firms deal with recurring client questions and complex compliance demands. Industry-tuned LLMs can:

  • Automate responses to billing, time tracking, or licensing inquiries.
  • Generate draft reports and compliance-ready documentation.
  • Help junior staff quickly access company playbooks or SOPs.
  • Free consultants to focus on higher-value client strategy.

The Five Pillars of Cybersecurity and Chatbots

When BALANCED+ evaluates how industry-specific chatbots fit into an organization, we consider five core areasour pillars of cybersecurity:

  1. Perimeter Security: Chatbots can help IT teams monitor VPNs, firewalls, and Wi-Fi environments, alerting them to unusual activity.
  2. Endpoint Protection: Chatbots integrated with EDR/MDR platforms can provide quick explanations or remediation steps when endpoints are flagged.
  3. Monitoring & Threat Hunting: With SIEM or SOAR integration, chatbots act as a natural-language interface for security analysts to query incidents or reports.
  4. Pentesting & Vulnerability Management: Chatbots trained on pentest reports can help leadership understand risks in plain English and prioritize fixes.
  5. Compliance & Governance: By encoding rules into the model, chatbots help employees stay compliantanswering Can we store this data in the U.S.? with confidence.

What to Consider Before Deploying a Specialized Chatbot

1. Data Security

Your chatbot must be trained and hosted in a way that keeps sensitive business and customer data safe. Using public LLMs without guardrails risks exposing proprietary information.

2. Integration with Systems

The chatbot should connect with your CRM, ERP, IT ticketing systems, or data warehouse. Without integration, it becomes another silo rather than a productivity booster.

3. Governance & Monitoring

Even industry-specific LLMs require monitoring to ensure accuracy. Establish a review process for ongoing fine-tuning and compliance checks.

4. Scalability

Choose solutions that can evolve as your business grows. A chatbot designed only for customer support today should be able to expand into compliance, internal knowledge management, or IT support tomorrow.


How BALANCED+ Can Help

BALANCED+ brings together 20+ years of consulting experience in cybersecurity, IT engineering, software development, and AI/ML. We help organizations design and implement industry-specific chatbot solutions that are secure, compliant, and deeply aligned with business goals.

Our approach includes:

  • LLM Training & Fine-Tuning: Using your industry data, policies, and workflows.
  • Secure Deployment: Ensuring compliance with privacy and data protection standards.
  • System Integration: Connecting chatbots with the tools your teams already rely on.
  • Continuous Monitoring & Optimization: Providing managed services to keep your chatbot accurate, secure, and evolving.
  • Strategic Roadmaps: Aligning chatbot adoption with your broader IT and digital transformation journey.

Why This Matters for Business Leaders

Cybersecurity and compliance challenges are only growing. Customers expect faster responses. Employees demand better tools. Regulators are tightening requirements.

Industry-specific chatbots powered by LLMs solve all three challenges:

  • They provide faster, more accurate answers for clients and staff.
  • They help ensure compliance with industry frameworks.
  • They reduce the burden on overstretched IT and security teams.

This is not a futuristic visionits already happening across healthcare, fintech, manufacturing, SaaS, and beyond.


Conclusion: Moving Beyond Generic AI

Generic chatbots were a useful first step, but theyre no longer enough. Businesses that want to stay competitive, and secure, must adopt intelligent, industry-trained chatbots that understand their unique risks, compliance needs, and workflows.

The future of chatbots isnt just conversation. Its trusted automation, powered by industry-specific LLMs.

Ready to explore how specialized chatbots can protect and transform your business? Contact BALANCED+ to start the conversation.

Extracting and Converting Maximizer CRM Emails

Maximizer CRM has been around for decades and is still widely used in legacy and mid-sized enterprises. While it continues to serve as a central hub for customer data, communications, and document storage, it poses unique challenges for those looking to modernize or migrate their environments.

One of the most frustrating problems comes when extracting emails from Maximizers SQL backend. Unlike modern CRMs that use standardized formats, Maximizer stores emails in multiple ways including a proprietary format that resists easy conversion.

In this post Ill walk through how I solved the problem of extracting hex encoded Email Message blobs from Maximizers database and converting them into standard .eml files with metadata and attachments intact.

How Maximizer Stores Emails

When exploring Maximizers backend I found emails in three formats:

  • .eml Standard MIME format
  • .msg Microsoft Outlook format
  • Email Message A Maximizer specific format that didnt behave like either of the above

Each was stored as a BLOB, often hex encoded in SQL. While .eml and .msg could be opened with some effort the Email Message files were undocumented, unreadable, and rejected by Outlook or other email clients.

The Breakthrough

After weeks of trial and error saving blobs as .msg files using Outlook interop and testing libraries like MSGReader or Independentsoft I noticed something important in the raw hex:

|xD0|xCF|x11|xE0

Thats the OLE Compound Binary File signaturethe same structure used by old Microsoft Office documents and Outlook .msg files.

But heres the twist: despite the familiar signature Maximizers format wasnt Outlook compatible. Attempting to deserialize still failed, leaving scrambled metadata or partial recoveries.

Treating It as a Generic OLE Container

The solution came by treating the file as a generic OLE compound container. Using the OpenMCDF library in C# I was able to explore the container directly.

Inside I found streams holding:

  • The full MIME message body
  • Attachments
  • Header metadata such as From, To, and Subject

With this data extracted I reconstructed the email into a standard .eml file using MimeKit.

Sample C# Code

using OpenMcdf;
using MimeKit;

public MimeMessage ParseMaximizerEmail(byte[] oleBytes)
{
    var compoundFile = new CompoundFile(new MemoryStream(oleBytes));
    var root = compoundFile.RootStorage;

    string mimeContent = Encoding.UTF8.GetString(root.GetStream("MIME").GetData());
    var message = MimeMessage.Load(new StringReader(mimeContent));

    return message;
}

Stream names like MIME or Body vary depending on the sample, so some trial and error is required.

Results

With this method I was able to:

  • Extract sender, recipients, subject, body, and attachments
  • Reconstruct readable .eml files for Outlook, Thunderbird, or any modern email client
  • Batch process and migrate thousands of Maximizer emails into Azure Blob Storage and Exchange Online

Challenges and Edge Cases

  • Encoding Issues Streams werent always UTF-8, sometimes UTF-16 appeared requiring detection logic
  • Embedded Content Images and nested attachments needed additional parsing
  • Incomplete Documentation Some OLE streams remain unexplained, requiring experimentation

Why This Matters

Maximizers proprietary Email Message format is a classic example of how undocumented storage can block migrations. Businesses stuck on legacy systems often feel trapped.

By using tools like OpenMCDF and MimeKit its possible to reverse engineer legacy structures and preserve critical communications in standard formats.

Final Thoughts

If youre planning a Maximizer migration or dealing with OLE-based email blobs in SQL, this approach can save you weeks of frustration. You can adapt the sample code for your own environment or reach out if youd like help modernizing your email archives.

Hybrid vs. Cloud-Based IT: Which One is Right for Your Business?

In today’s digital landscape, businesses are constantly evaluating the best IT infrastructure to support their operations, enhance security, and optimize costs. Two of the most popular models are hybrid IT and cloud-based IT, each offering distinct advantages and challenges. Understanding the differences and choosing the right model can significantly impact your businesss efficiency and scalability.

What is Cloud-Based IT?

Cloud-based IT refers to computing resources that are fully hosted in the cloud, managed by a third-party provider, and accessed via the internet. Businesses using cloud-based IT benefit from:

  • Scalability: Cloud solutions can scale up or down depending on demand, ensuring optimal resource usage without excess costs.
  • Cost Efficiency: Instead of investing in costly hardware and maintenance, businesses pay for what they use, transforming capital expenditures into operational costs.
  • Innovation and Accessibility: Cloud providers frequently introduce new technologies, such as AI-driven analytics and automation, giving businesses access to cutting-edge tools.
  • Security and Compliance: Major cloud providers implement robust security measures, but businesses must ensure compliance with industry regulations and data protection policies.

Pros and Cons of Cloud-Based IT

Pros:

  • Lower upfront costs and predictable pricing
  • Rapid scalability and easy resource allocation
  • Reduced IT management burden
  • Advanced security features from cloud providers

Cons:

  • Less control over data and infrastructure
  • Potential latency or performance issues depending on location
  • Higher long-term costs if not managed properly
  • Compliance challenges in highly regulated industries

What is Hybrid IT?

Hybrid IT is a combination of on-premises infrastructure and cloud solutions, allowing businesses to retain some workloads and sensitive data on their own servers while leveraging the cloud for other applications. The hybrid approach offers:

  • Flexibility and Control: Organizations can keep mission-critical applications and sensitive data on-premises while utilizing the cloud for scalability and performance.
  • Cost Management: Businesses can optimize costs by balancing workloads between on-premises and cloud environments.
  • Enhanced Security: Certain industries require strict data protection policies that can be more effectively managed with on-premises solutions while still benefiting from cloud efficiencies.
  • Customization: Organizations can tailor their IT infrastructure to their specific needs, ensuring a balance between security, performance, and cost-effectiveness.

Pros and Cons of Hybrid IT

Pros:

  • Greater control over sensitive data
  • Flexibility to balance workloads efficiently
  • Improved disaster recovery options
  • Compliance with industry-specific regulations

Cons:

  • More complex to manage than a fully cloud-based solution
  • Potential integration challenges between on-premises and cloud systems
  • Higher upfront costs for maintaining local infrastructure

Key Statistics and Industry Trends

  • 81% of enterprises have a multi-cloud strategy, and 67% use hybrid cloud solutions to balance flexibility, security, and cost. (Flexera 2023 State of the Cloud Report)
  • 94% of enterprises already use a cloud service, indicating the widespread adoption of cloud-based IT. (Flexera)
  • 45% of businesses say security is a primary concern in cloud migration, making hybrid IT a viable option for those needing extra control. (Gartner)

Which One is Right for Your Business?

The decision between hybrid IT and cloud-based IT depends on your businesss specific needs:

  • Choose Cloud-Based IT if: You prioritize scalability, cost efficiency, and rapid deployment of new technologies without the burden of managing on-premises hardware.
  • Choose Hybrid IT if: You need to maintain control over sensitive data, comply with strict regulations, or optimize costs between cloud and on-premises resources.

Conclusion

Both hybrid and cloud-based IT infrastructures offer valuable benefits depending on business goals, regulatory requirements, and IT management capabilities. By assessing your needs in terms of security, cost, scalability, and control, you can determine which approach aligns best with your organizations long-term strategy.

Whether fully embracing the cloud or integrating a hybrid model, investing in the right IT infrastructure will help drive business growth, improve efficiency, and ensure secure operations in the evolving digital landscape.

Trump Announces Tariffs: What It Means for Consultants

The recent wave of proposed tariffs imposed by the United States on Canadian and Mexican imports has ignited concerns across multiple industries. While much of the focus has been on manufacturers, supply chain disruptions, and trade negotiations, one crucial sector that often gets overlooked in these discussions is professional services, including consulting.

Unlike physical goods, which can be taxed at the border, professional services remain largely unaffected by tariffs. However, the ripple effects of these economic policies can significantly alter the landscape in which consultants operate. So, what do these tariffs mean for consulting firms and independent professionals?

Understanding the New Tariffs

On February 1, 2025, the U.S. administration announced fresh tariffs on imports from Canada, Mexico, and China. For Canada, this meant a 25% tariff on most goods and a 10% tariff on energy products. However, following negotiations, these tariffs have been temporarily paused for Canada and Mexico, delaying their implementation until March 4, 2025. This delay was agreed upon after discussions with Canadian and Mexican leaders, during which both countries committed to enhancing border security and addressing concerns related to illegal immigration and drug trafficking.

While professional services, such as consulting, are not subject to these tariffs, the broader economic impact cannot be ignored. Consultants advising clients in industries directly affected by tariffs must quickly adapt to the shifting financial realities of their clients.

Why Professional Services Are Exempt

The nature of consulting and other professional services makes them difficult to tariff. Unlike goods that physically cross borders and can be taxed at customs, consulting is largely intangible. There is no clear mechanism for tracking or taxing a service that is performed remotely or delivered digitally.

Additionally, international agreements, such as those under the USMCA (United States-Mexico-Canada Agreement), encourage the free flow of services between countries. Imposing tariffs on services would likely conflict with these agreements, leading to further complications in trade relations.

The Indirect Impact on Consultants

Even though consulting services themselves are not tariffed, the industries that consultants serve are often directly affected. Here are a few key ways consultants might feel the impact:

1. Increased Client Costs and Budget Constraints

With the cost of imported goods rising, businesses that rely on cross-border trade will see their expenses increase. This can lead to tighter budgets, making companies more cautious about hiring external consultants. Some firms may delay or cancel projects, opting to handle business strategy and process improvements in-house rather than outsourcing them to experts.

2. Demand for Trade and Supply Chain Consulting

Conversely, some consultants may see a surge in demand for their expertise. Companies facing supply chain disruptions or exploring alternative sourcing options will need guidance on restructuring their operations. Consultants with experience in logistics, procurement, and trade compliance will be in high demand as businesses look for ways to mitigate the financial impact of tariffs.

3. Regulatory and Compliance Changes

New trade policies mean new compliance challenges. Businesses must ensure they are adhering to the latest regulations, which could lead to an increased demand for consultants specializing in regulatory affairs and international trade law. Companies will need guidance on how to adapt to evolving tariff structures, ensuring they remain compliant while optimizing their financial strategies.

4. Cross-Border Consulting Challenges

For Canadian consultants serving U.S. clients, shifting economic policies could impact how business is conducted. While professional services are not subject to tariffs, firms working closely with tariffed industries may experience changes in contract terms, pricing negotiations, and even the willingness of U.S. companies to engage with Canadian consultants.

The Future of Tariffs and Professional Services

Despite the current focus on taxing goods, there is an ongoing global discussion around digital service taxes and other mechanisms that could eventually impact consulting services. However, as of now, services remain largely outside the scope of tariff regulations.

That said, consultants must stay informed about trade developments, not only to advise their clients effectively but also to understand the potential long-term risks to their own businesses. The ability to navigate economic shifts and provide strategic insights will separate successful consulting firms from those struggling to adapt.

Final Thoughts

While the direct impact of tariffs on consulting is minimal, the indirect effects can be substantial. Consultants working with affected industries must be proactive in understanding how trade barriers reshape business strategies. Those who position themselves as trusted advisors in navigating these changes will find new opportunities amid the challenges.

As the U.S.-Canada tariff situation continues to evolve, professionals across industries must remain agile. For consultants, this means being at the forefront of changeoffering solutions, mitigating risks, and helping businesses adapt to a rapidly shifting economic landscape.

Biggest Changes in Fortinet FortiOS 7.2.1

Exploring the Changes

Fortinets FortiOS 7.2.1 brings a host of updates that redefine network security, management, and performance. These enhancements aim to improve functionality across various facets of network operations, ensuring organizations stay secure and efficient. Lets explore the biggest changes introduced in this release.

Need help selecting the right FortiGate for your business? Take our quiz:

Struggling To Choose The Right Fortigate?

Take our quick quiz to get a personalized suggestion for your business.

Start Quiz
Modern abstract graphic representing potential or growth

1. FortiClient EMS Integration

This update streamlines endpoint management with predefined connectors for up to five FortiClient EMS instances. Administrators can now configure status, names, and display tenant IDs, providing greater flexibility and clarity in managing endpoints. Learn more here.


2. Procend 180-T DSL Transceiver Support

FortiGate devices now support the management of Procend 180-T DSL transceivers connected via SFP ports. Administrators can program physical layer attributes, retrieve status, monitor statistics, perform firmware upgrades, and reset modules. Supported VDSL profiles include 8a, 8b, 8c, 8d, 12a, 12b, 17a, and 30a. Supported models include FG-80F, FG-81F, FG-80F-BP, FGR-60F, and FGR-60F_3G4G. More details here.


3. FortiView Internal Hubs Monitor

A new FortiView page now displays internal host connections based on NetFlow data from managed switches. This feature provides insights into device connections and traffic patterns. The FortiLink interface can be configured as a NetFlow collector to enable this functionality. Find out more.


4. IPv6 Support in Cisco ACI SDN Connectors

FortiGate now supports IPv6 dynamic addresses retrieved from Cisco ACI SDN connectors. These addresses can be integrated into dynamic address objects for firewall policies, enhancing IPv6 capabilities. Note that this requires Fortinet SDN Connector VM version 1.1.10 or later. Read more here.


5. Internet Service Database (ISDB) Enhancements

IPv6 addresses are now supported in ISDB via the CLI, allowing for expanded IPv6 configuration in firewall policies. This improvement bolsters FortiGates IPv6 capabilities. More information available here.


6. FortiNAC Integration via REST API

A new REST API enables FortiNAC to send user logon/logoff information to FortiGate. This introduces a dynamic firewall address type (FortiNAC tag) to store device IPs, firewall tags, and group information. Note that the FortiNAC tags connector under Security Fabric > Fabric Connectors has been deprecated. Details here.


7. Security Rating PSIRT Vulnerability Support

FortiGate devices with a valid Security Rating license now include a separate Security Rating package from FortiGuard, adding support for PSIRT vulnerabilities. Critical vulnerabilities trigger warning messages in the GUI header and notifications, encouraging timely updates for affected devices. Learn more.


8. ZTNA Service Discovery for FortiClient

FortiClients can now discover available ZTNA services via the FortiGate ZTNA portal. Supported services include HTTP/HTTPS web services, TCP forwarding services, and web portals. This discovery occurs through DoT or DoH tunnels, with service mappings retrieved in JSON format. More on this here.


9. RADIUS Accounting Message Delimiter Option

Administrators can now configure the RADIUS accounting message group delimiter to a comma (,) instead of the default plus sign (+) when using RSSO. This added flexibility enhances compatibility with different systems. Further details here.


10. Internet Service Database Size Options

FortiOS 7.2.1 introduces three sizes for internet service databasesfull, standard, and mini. The mini size is configurable on FortiGate 30 and 50 series models, allowing database optimization based on device capabilities. Explore more.


11. Enhanced IP Address Management (IPAM)

The GUI and CLI now support multiple IPAM pools, enabling administrators to assign these pools to different interfaces based on name and/or role using IPAM rules. This update improves IP address management flexibility and efficiency. Details here.


12. YAML Configuration Backup/Restore

YAML can now be selected as a file format for configuration backup and restoration. This provides an alternative to traditional formats, catering to organizations that prefer YAML for its readability and versatility. Learn more here.


Conclusion

The updates in FortiOS 7.2.1 showcase Fortinets commitment to innovation in network security and management. From enhanced endpoint and IP address management to expanded IPv6 support and streamlined vulnerability tracking, these features empower organizations to strengthen their security posture while improving operational efficiency. Explore these updates further to ensure your network remains ahead of evolving cyber threats.

Interested in leaning more? Contact us today to see how BALANCED+ can help implement Fortinet into your security infrastructure